ARP®
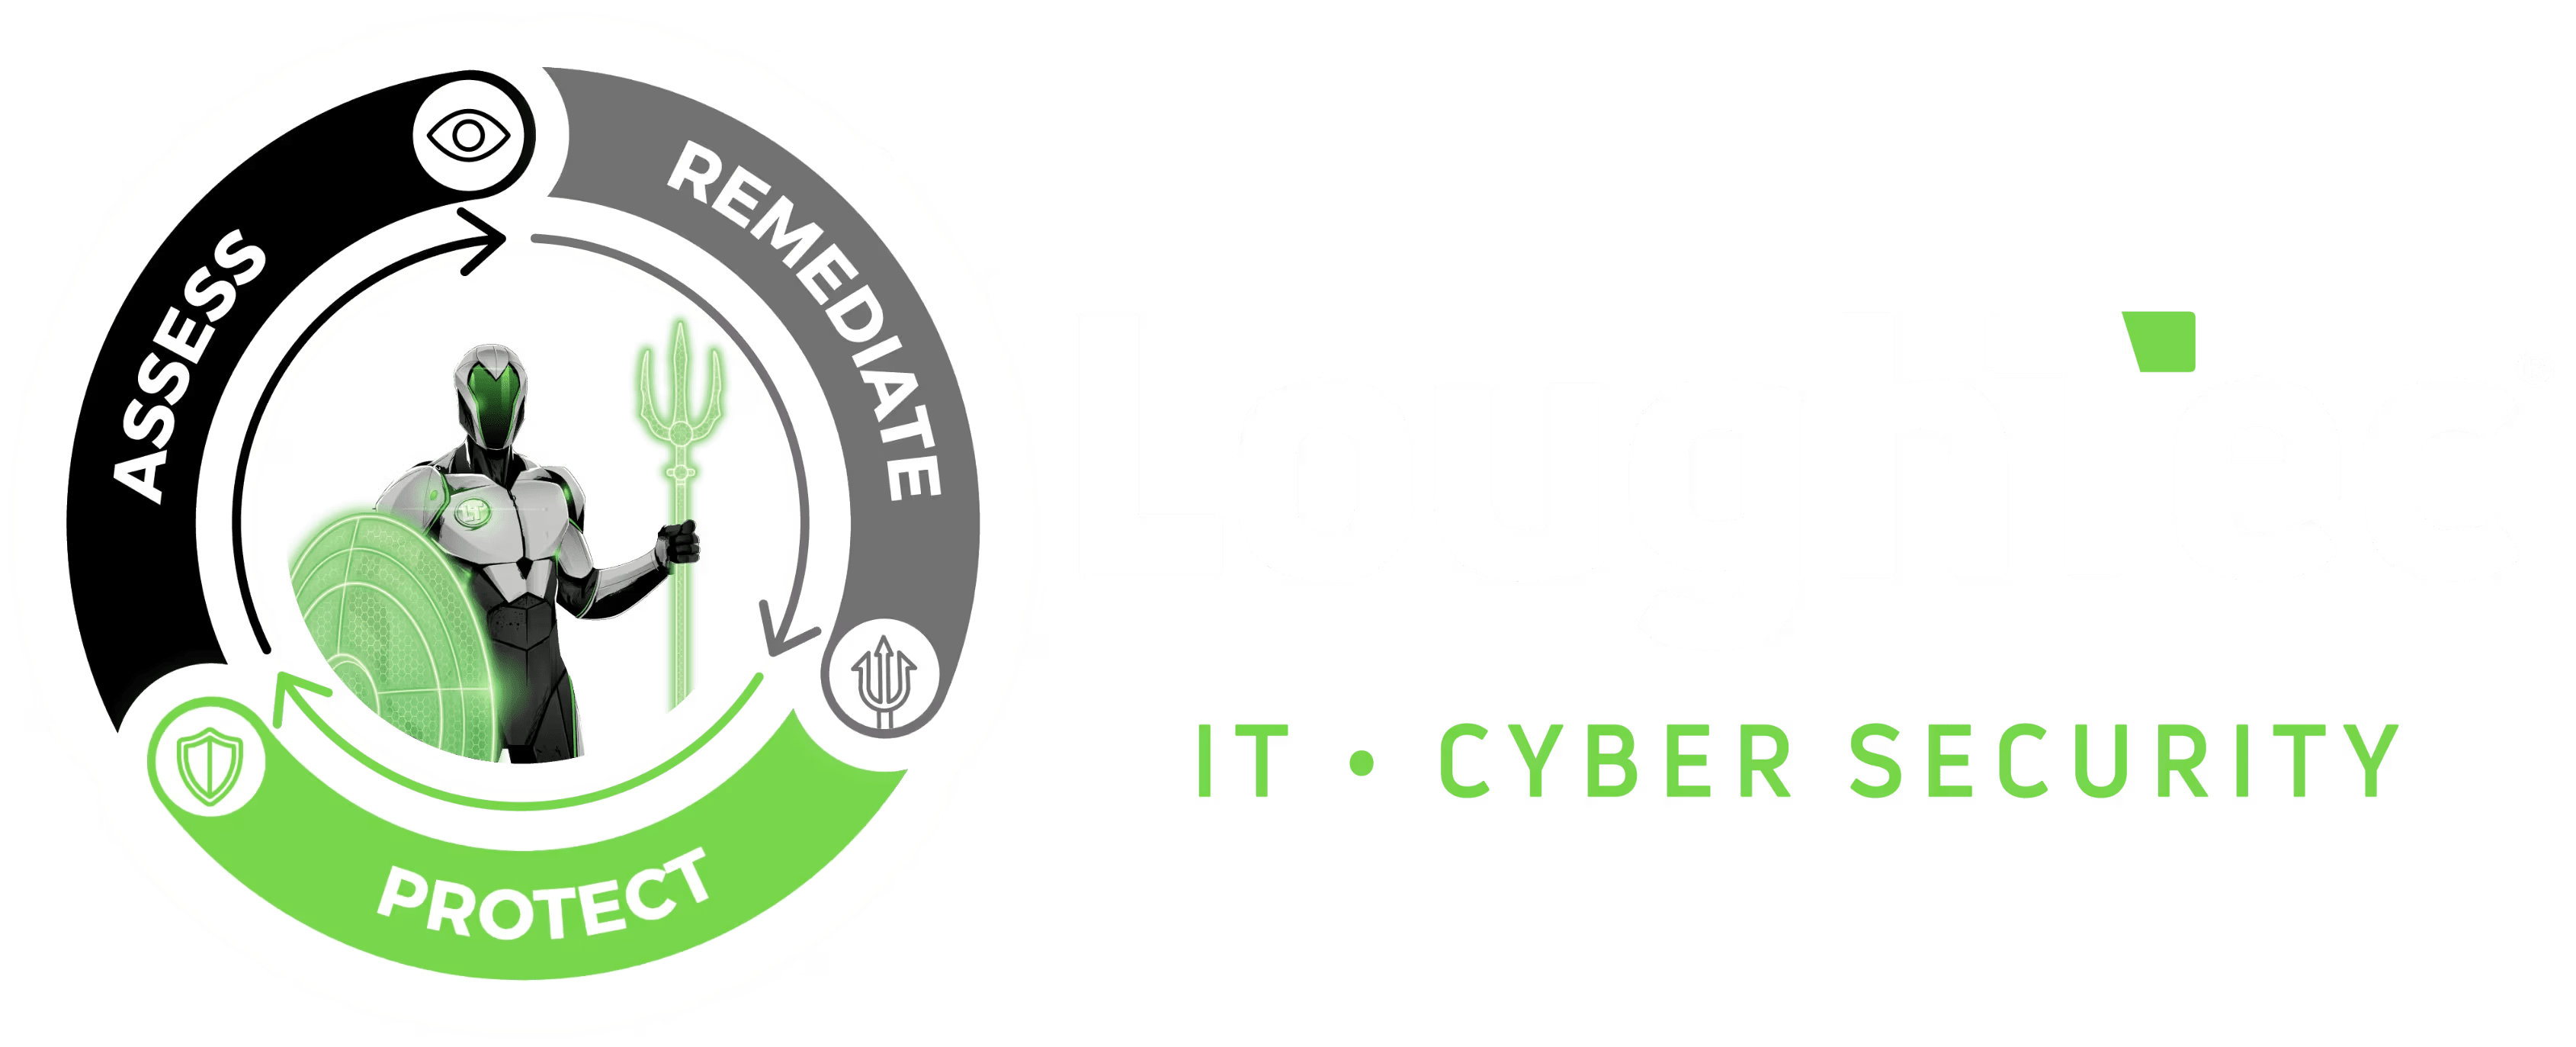
Assess. Remediate. Protect.
A Clearer Path to Cyber Maturity and Resilience
Most organisations have security tools. Fewer have a strategy.
ARP® gives you both, a structured, repeatable framework that continuously identifies your risks, reduces them, and keeps you protected as threats evolve.
Cyber threats evolve every day. Deploying antivirus software, a firewall or even Microsoft 365 security features won’t protect your organisation if those tools don’t work together as part of a coherent strategy.
ARP® = Assess. Remediate. Protect. is LoughTec’s proprietary cyber security framework, built to give organisations of all sizes a practical, risk-based roadmap for building and maintaining strong cyber defences.
Rather than asking “What products should we buy?”,
ARP® answers the questions that actually matter:
Where are our greatest cyber risks?
- We find them before attackers do.
How do we reduce those risks?
- We prioritise fixes by business impact, not technical complexity.
How do we stay protected as threats change?
- We monitor, adapt and improve continuously.
The result is measurable progress, not just more technology.
The Three Stages of ARP®
STAGE ONE
ASSESS
Understand Your Cyber Security Posture
You can’t protect what you don’t understand.
The first stage is a thorough assessment of your current security environment for infrastructure, cloud services, Microsoft 365, devices, networks and access controls. Our consultants identify vulnerabilities before they can be exploited, and deliver findings in a prioritised risk report your leadership team can act on.
Assessments might typically cover:
• Microsoft 365 Security Reviews
• Cyber Security Maturity Assessments
• External Attack Surface Reviews
• Dark Web Exposure Checks
• Firewall and Network Security Reviews
• Email and DNS Security Assessments
• Backup and Disaster Recovery Validation
• Identity and Access Management Reviews
• Compliance Readiness Assessments
The output isn’t a list of technical findings, it’s a clear picture of where you stand and a future roadmap of what to do next.
STAGE TWO
REMEDIATE
Reduce Risk via Targeted Improvements
Identifying vulnerabilities is only the start.
The Remediate stage turns assessment findings into concrete security improvements, prioritised by business impact so your most critical risks are addressed first. Every recommendation is tied to a measurable reduction in exposure not simply adding another layer of technology.
Typical remediation work may include:
• Microsoft 365 Security Hardening
• Multi-Factor Authentication (MFA) and Conditional Access
• Endpoint Detection and Response (EDR)
• Advanced Threat Protection
• DNS Filtering and Firewall Optimisation
• Backup Modernisation and Disaster Recovery Planning
• Staff Security Awareness Training
• Device Encryption and Identity Protection
We work at your pace and budget, building a stronger security posture progressively and sustainably.
STAGE THREE
PROTECT
Continuous Cyber Protection
Cyber security is never finished.
The Protect stage keeps your defences both active and up to date, whilst ensuring proactive monitoring of your digital estate, rapid threat detection and isolation against serious threats and attacks especially ransomware, along with regular reviews and roadmaps that adapt to new changes in technology and risks as they emerge.
Protection services may include:
• Security Operations Centre (SOC)
• Managed Detection and Response (MDR)
• Continuous Vulnerability Management
• Dark Web Monitoring
• DNS Monitoring & Filtering
• Managed Firewall Protection
• Microsoft 365 Protection
• Incident Response
• Compliance Monitoring
• Regular Security Reviews
This ongoing layer means threats are caught early, response times are faster, and the impact of any incident is minimised.
The Continuous Improvement Cycle
ARP® isn’t a one-off project. It’s a continuous improvement cycle.
Assess → Remediate → Protect → Assess again
As your organisation grows, as technology changes, and as new threats emerge, your security strategy evolves alongside them. This cycle is what separates organisations that stay resilient from those that only react after an incident.
Supporting Compliance and Governance
The ARP® Framework assists security improvements with recognised standards and regulatory requirements, helping you meet your obligations while genuinely improving resilience.
Frameworks and standards ARP® assists with
• Cyber Essentials and Cyber Essentials Plus
• ISO 27001
• NIS2
• DORA
• UK GDPR
• PCI DSS
Compliance and strong security aren’t the same thing, but the controls implemented through ARP® support both.
Why Organisations Trust LoughTec
LoughTec has been protecting businesses across Northern Ireland, Ireland and the UK for over 20 years. We combine experienced cyber security professionals, enterprise-grade technology and a proven methodology to deliver outcomes that matter:
Reduced cyber risk
- measurable, not just theoretical
Improved resilience
- so incidents have less impact, when they occur
Secure growth
- so your security posture keeps pace with your business
We are ISO 27001 certified, and our focus has always been practical security that works, not complexity for its own sake or for a tick box.
Frequently Asked Questions
ARP® stands for Assess. Remediate. Protect. It is LoughTec’s registered trademark and proprietary cyber security methodology, developed over years of working with organisations across a wide range of sectors and sizes.
Yes. ARP® scales from growing SMEs through to larger enterprise environments. The framework is designed to meet you where you are, whether you’re starting from scratch or building on existing security investments.
Absolutely. ARP® can complement your current IT support provider or function as a fully managed cyber security service delivered by LoughTec, the approach is flexible to suit your setup.
ARP® significantly reduces both the likelihood and impact of ransomware attacks through layered assessment, targeted remediation and continuous 24/7 monitoring. No framework can guarantee absolute protection, but organisations that follow a structured, ongoing programme are demonstrably better protected than those relying on standalone tools.
Every ARP® engagement begins with an assessment of your current cyber security posture. From there, we produce a prioritised roadmap tailored to your organisation, so you know exactly where to focus and why. The first step is a conversation.
Cyber threats aren’t standing still. Neither should your security strategy.